At the 2026 TAA ONE Conference, one of the most gripping sessions didn’t come from a traditional business leader. It came from someone who once operated on the other side of the system entirely.
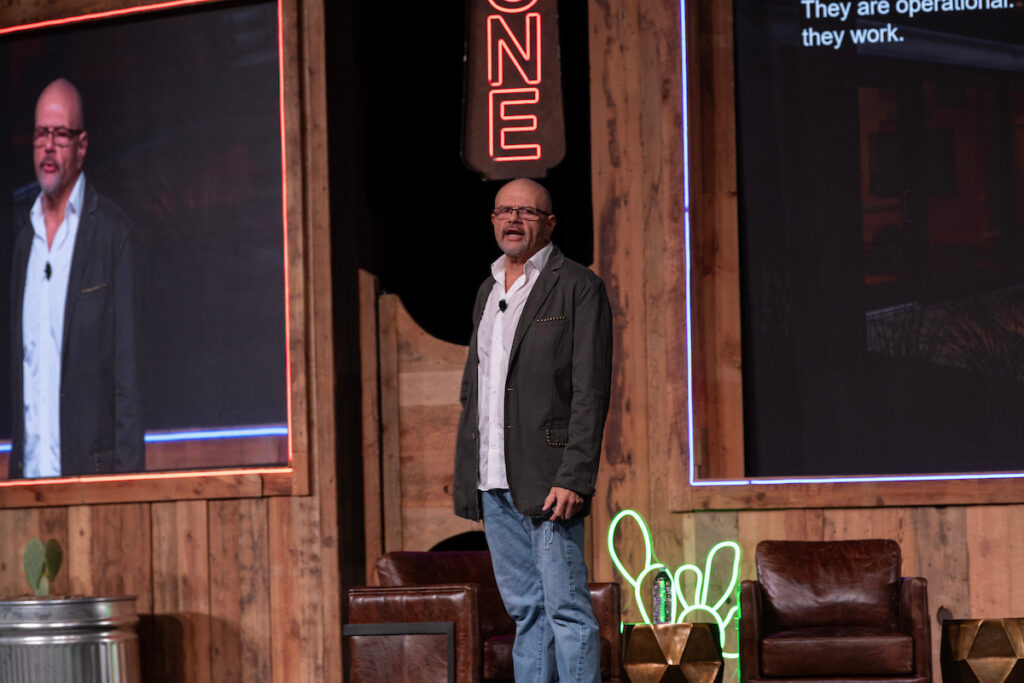
Brett Johnson, once named the “Original Internet Godfather” by the United States Secret Service, took the stage to share a perspective few organizations ever get: how cybercriminals actually think, operate, and exploit weaknesses. His message wasn’t theoretical. It was practical, uncomfortable, and incredibly relevant.
The Mindset of a Cybercriminal
Johnson didn’t start with systems or technology. He started with something much more fundamental: trust. “When I was committing fraud,” he explained, “the first step was always to get people to trust me.”
That insight reframes how many organizations think about cybersecurity. It’s not just about firewalls, software, or policies. It’s about people, behavior, and the small moments where trust is extended—often too quickly.
Johnson knows this firsthand. As the founder of ShadowCrew, one of the first organized cybercrime communities, he helped shape the early playbook for modern financial cybercrime. After being arrested, escaping prison, and ultimately being given a second chance, he now works with major organizations and law enforcement to prevent the very crimes he once committed. In 2024 alone, he assisted the FBI with over 300 cybercrime arrests.
Criminals Don’t Hack Companies. They Exploit Processes.
One of the most important takeaways from the session was this: Criminals don’t beat the biggest company. They beat the easiest process. In other words, size and scale don’t protect you. Consistency and discipline do.
Johnson emphasized that cybercriminals aren’t looking for the most sophisticated target; they are looking for the weakest link. And that weakness often exists in the gap between what a company says its policies are and what actually happens day to day. “There’s a difference between a written policy and the real policy,” Johnson said. “Criminals operate in that gap.”
Where Vulnerabilities Actually Come From
Many leaders assume fraud happens because of complex technical failures. Johnson challenged that assumption. Instead, he pointed to three primary conditions that create openings for fraud: Speed, inconsistency, and exceptions. When teams are rushed, standards vary, or exceptions are routinely made, risk increases dramatically.
Johnson pointed out that a criminal doesn’t need a perfect fake. They need a rushed reviewer. That line landed hard, and for good reason. In industries like multifamily, where teams are balancing leasing, operations, residents, and vendors, speed is often prioritized over scrutiny. But that’s exactly what bad actors are counting on.
How Modern Cybercrime Actually Happens
Johnson broke down a common and surprisingly simple attack path. Most cybercrime begins with a phishing email. From there, criminals research their target using publicly available information like LinkedIn profiles, social media, and company websites. They learn how the business operates, who the vendors are, and how communication flows. Then they strike.
They impersonate a trusted vendor, often using a nearly identical email address, and insert themselves into an existing conversation. A small change, like a missing dot over an “i”, is all it takes. From there, urgency does the rest. Social engineering works not because people are careless, but because it exploits normal human behavior: urgency, authority, routine, fatigue, and even empathy.
The Real Cost of Pressure
Johnson noted that global cybercrime damage costs have reached $10 trillion, and if cybercrime were measured as a country, this economic impact would make it the world’s third-largest economy, trailing only the U.S. and China.
Another powerful theme from the session was the role of organizational pressure. When teams are pushed to move faster, close deals, or “just get it done,” they’re more likely to bypass safeguards. That creates openings not just for fraud, but for broader operational issues like bad debt, burnout, resident distrust, and brand risk. He made it clear: leadership plays a critical role here. If the culture doesn’t allow people to pause, question, and verify, then the system itself is vulnerable.
Five Rules That Actually Work
Rather than offering abstract advice, Johnson left the audience with five practical rules that simple, operational, and effective:
- Slow down high-risk decisions
- Verify through a second channel
- Eliminate unnecessary exceptions
- Give staff permission to say no
- Standardize across properties
These aren’t complex solutions, and that’s exactly why they work. Consistency beats complexity every time.
One Standard. One Target.
For multifamily operators managing multiple properties, Johnson emphasized the importance of standardization. “One portfolio. One standard. One hard target.” When processes vary from property to property, criminals will find the weakest one and start there. But when standards are consistent, the organization becomes significantly harder to penetrate.
A Perspective You Can’t Ignore
What made this session so impactful wasn’t just the content; it was the credibility. Johnson openly acknowledged that while he’s been on the right side of the law for over a decade, the mindset doesn’t disappear. He is still often faced with temptations, thought patterns, and tactics. That perspective gives leaders something incredibly valuable: insight into how attacks actually happen, and how to stop them.
The Bottom Line for Leaders
Cybersecurity isn’t just an IT issue. It’s an operational issue, a leadership issue, and a culture issue. The biggest risks don’t come from advanced technology. They come from everyday decisions, small inconsistencies, and moments of pressure.
And the solution isn’t to add more complexity. It’s to build better habits. Because at the end of the day, criminals aren’t looking for the biggest target. They’re looking for the easiest one.